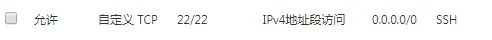有的时候服务/软件配置没有问题,就是无法访问,可能是你没有在主机上开放对应的端口。
防火墙设置
Error:注意:出于安全考虑不建议关闭防火墙!
centos命令:
 1#开放对应tcp端口
 2firewall-cmd --zone=public --add-port=80/tcp --permanent
 3#开放对应udp端口
 4firewall-cmd --zone=public --add-port=80/udp --permanent
 5#防火墙重载配置
 6firewall-cmd --reload
 7
 8#临时关闭防火墙(不推荐)
 9systemctl disable firewalld
10#禁用防火墙(不推荐)
11systemctl stop firewalld
通用命令:
Error:注意:出于安全考虑不建议关闭防火墙!
 1#编辑防火墙规则
 2sudo vim /etc/sysconfig/iptables
 3
 4#添加22端口tcp协议规则
 5iptables -A INPUT -p tcp --dport 22 -j ACCEPT
 6iptables -A OUTPUT -p tcp --sport 22 -j ACCEPT
 7#添加22端口udp协议规则
 8iptables -A INPUT -p udp --dport 22 -j ACCEPT
 9iptables -A OUTPUT -p udp --sport 22 -j ACCEPT
10
11#检查防火墙规则
12iptables -L -n
13
14#保存防火墙的设置
15serivce iptables save
16
17#重启防火墙
18service iptables restart
19
20#永久开启防火墙
21chkconfig iptables on
22#永久关闭防火墙
23chkconfig iptables off
24
25#临时开启防火墙
26service iptables start
27#临时关闭防火墙
28service iptables stop
云服务器控制台
这里以阿里云为例。
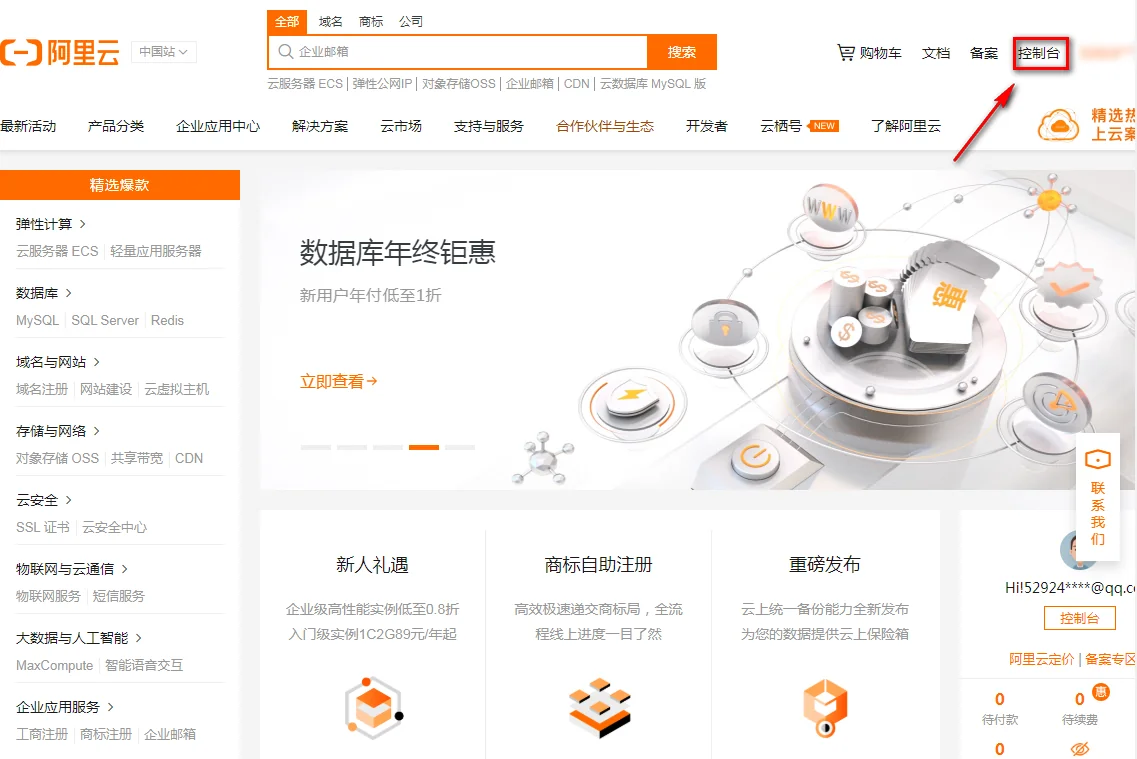
1. 首先打开控制台
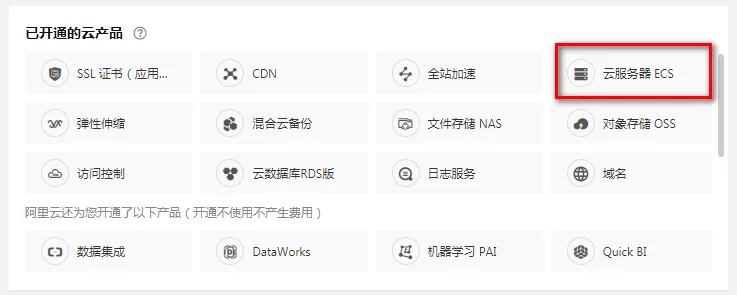
2. 打开云服务器ECS
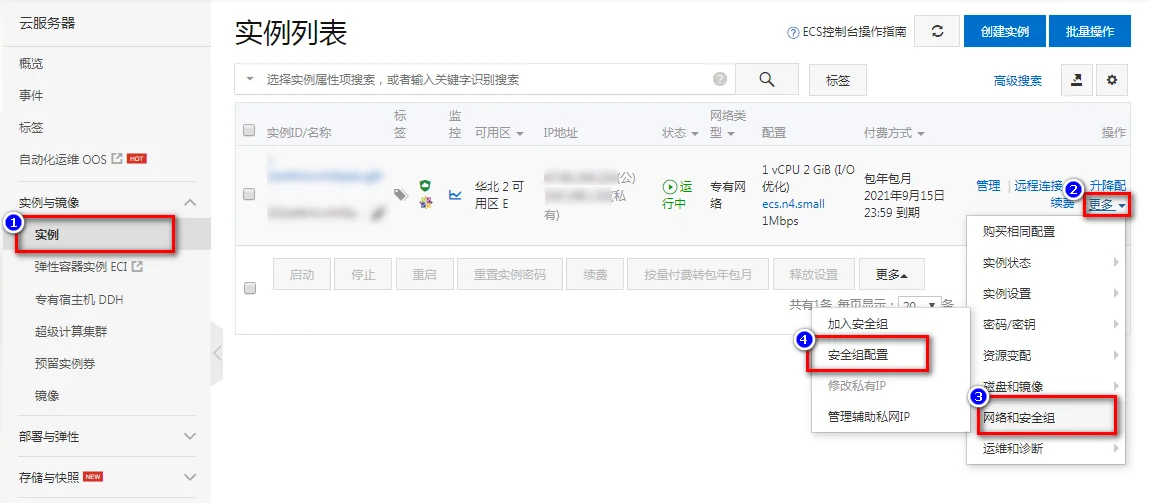
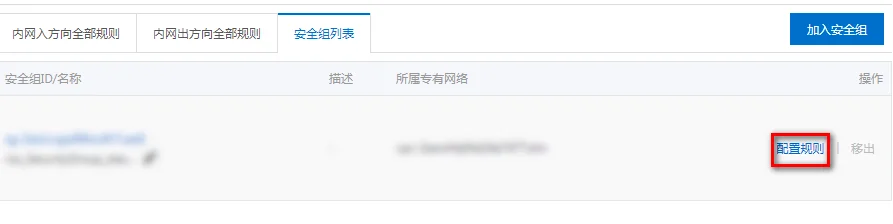
3. 打开对应服务器的安全组
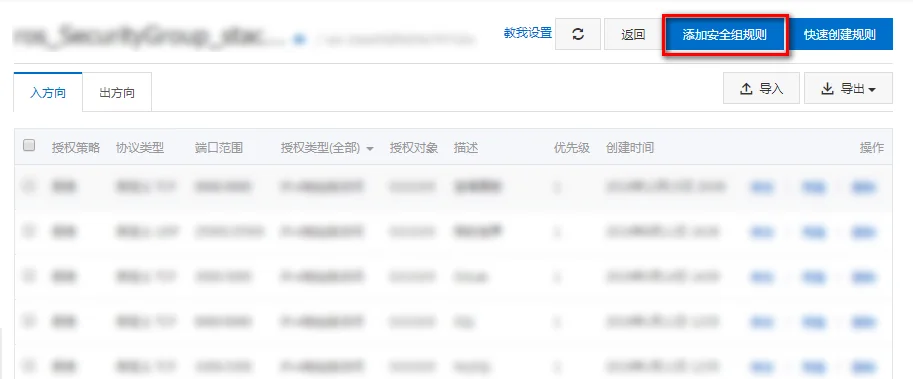
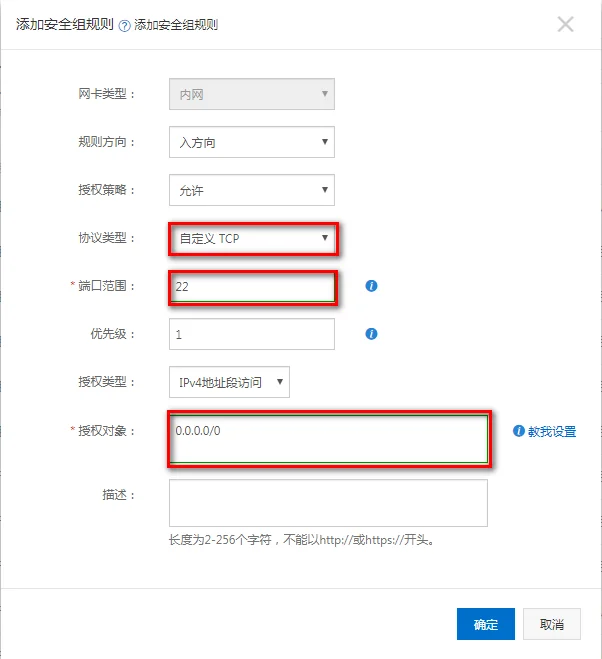
4. 添加规则(出方向默认全放行,只管理入方向即可)
5. 查看效果